
Chapter 2 of 6
Architecture at a glance#
One external approval maps to one Azure child deployment. deployment-profiles.json carries the settings needed by preflight and Bicep. Preflight checks the exact Foundry scope, operator role, model availability and lifecycle, Responsible AI policy, processing location, quota, and resource-scoped what-if. A mismatch stops the run.
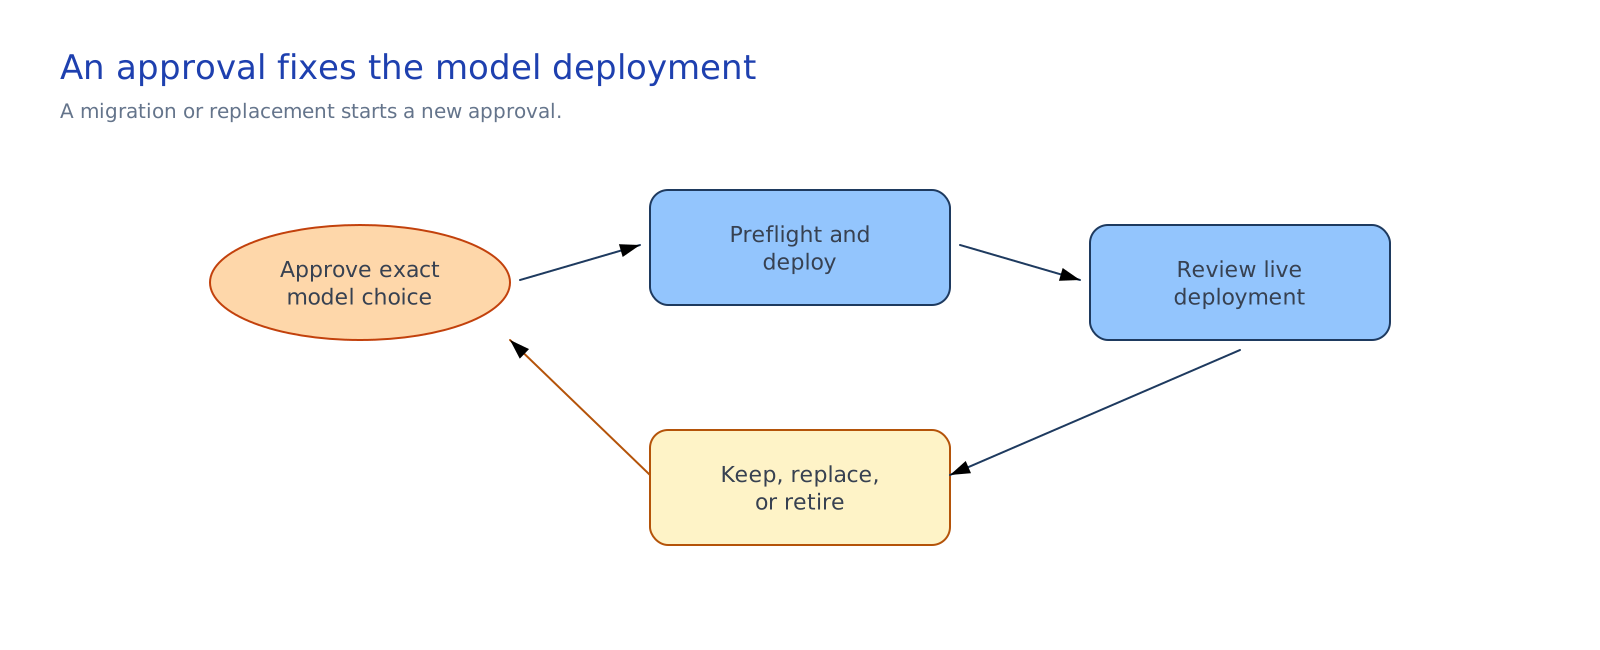
The deployment profile pins the model version with NoAutoUpgrade. The governed-agent deployment consumes the approved deployment name and model coordinates.
The approval register records the approved publisher, asset ID, source, hosting route, review decision, and processing-location boundary. The policy parameter file reads its allowed values, so the policy assignment and approval decision stay aligned.
Design choices and tradeoffs#
| Decision | Chosen approach | Cost or limit |
|---|---|---|
| Approval record | Keep the full review in the decision system and deployment inputs in Git | The approval ID must match both systems |
| Service facts | Read lifecycle, availability, quota, and the named Responsible AI policy during preflight | Missing CLI fields require a named manual check |
| Version changes | Pin exact coordinates with NoAutoUpgrade | The owner must start replacement before retirement |
| Deployment policy | Assign the built-in approved-model and eligibility policies from the approval register | Audit needs review before Deny blocks a deployment |
| Control reach | Govern this version-controlled deployment path | Other authorized paths remain open |